Webflow is not just a visual design tool. Behind the drag-and-drop interface lies a production-grade infrastructure stack that most agencies and clients never fully examine before committing to the platform. Understanding what actually happens when Webflow serves your site — where files live, how requests are routed, what security layers exist, and how performance is handled at scale — is essential for making informed architectural decisions, especially when your site is carrying real business weight.
This post breaks down Webflow's infrastructure from a technical standpoint: what it does well by default, where the constraints are, and how a well-structured Webflow project can be engineered to perform at a level comparable to custom-built stacks.
Webflow Hosting Infrastructure: What You're Actually Getting
Webflow hosts all published sites on Amazon Web Services (AWS), with static assets served through Fastly, one of the most capable CDN providers in the industry. When you publish a Webflow site, the platform compiles your design into clean HTML, CSS, and JavaScript, then distributes that output across Fastly's global edge network. This means your site is not running on a traditional origin server waiting for requests — it's pre-rendered and cached at the edge, geographically close to the end user.
This architecture has significant implications:
- No server-side rendering latency for standard Webflow pages. The HTML is already built and cached.
- No database queries on page load for static pages. CMS content is baked into the HTML at publish time.
- Automatic redundancy through AWS and Fastly's multi-region infrastructure.
- Zero server management — no patches, no capacity planning, no PHP version conflicts.
Fastly CDN: Edge Caching Behavior
Fastly operates on a pull-through cache model with edge nodes distributed across North America, Europe, Asia-Pacific, and Latin America. When a user requests a Webflow page:
- The request hits the nearest Fastly edge node.
- If the asset is cached at that edge, it's served immediately — typically in single-digit milliseconds.
- If the cache is cold (post-publish or post-invalidation), Fastly fetches from AWS origin and caches the response for subsequent requests.
Webflow automatically purges the Fastly cache on every publish, ensuring users always receive the latest content. For teams running high-frequency CMS updates, this means cache invalidation is handled without any manual intervention or infrastructure configuration.
Custom Domains and SSL
Webflow provisions SSL certificates automatically via Let's Encrypt for all custom domains connected to a paid hosting plan. Certificate renewal is handled by the platform, eliminating one of the most common sources of site downtime on self-managed stacks. HTTPS is enforced by default, and HTTP requests are automatically redirected to HTTPS at the CDN level — not via application-layer redirects that add latency.
For enterprise clients requiring wildcard certificates, custom certificate authorities, or more granular TLS configuration, Webflow's Enterprise plan provides options that go beyond the standard Let's Encrypt provisioning. This is a relevant consideration for B2B companies with strict security procurement requirements.
Bandwidth and Uptime SLAs
Webflow's hosting plans include unmetered bandwidth on Business and Enterprise tiers. The platform publishes a 99.99% uptime SLA for Enterprise customers, backed by AWS's underlying infrastructure guarantees. For most B2B web projects — marketing sites, CMS-driven content hubs, product pages — this infrastructure is genuinely overbuilt relative to what a typical VPS or shared hosting environment would provide.
The trade-off is control. You cannot modify server headers beyond what Webflow exposes in its settings, cannot install server-side middleware, and cannot run background processes or server-side logic natively. For sites that need those capabilities, the right architectural response is to push that logic to external services — APIs, serverless functions, middleware platforms — and connect them to Webflow via custom code embeds or the Webflow API.
Performance Engineering on Webflow: Beyond the Default
Webflow's default output is reasonably performant, but "reasonably performant" is not the same as "optimized for Core Web Vitals." The platform handles image optimization, asset minification, and CDN delivery automatically, but the decisions made during the build — class architecture, interaction design, third-party script loading, font strategy — have an outsized impact on real-world performance metrics.
Core Web Vitals and What Webflow Controls
Google's Core Web Vitals framework measures three primary signals: Largest Contentful Paint (LCP), Cumulative Layout Shift (CLS), and Interaction to Next Paint (INP). Webflow's infrastructure directly supports good scores on all three, but only if the project is built correctly.
LCP is primarily affected by:
- Hero image size and format. Webflow serves images via its own CDN and supports WebP conversion, but you need to upload appropriately sized source images and configure responsive image settings correctly.
- Font loading strategy. Loading multiple font weights from Google Fonts or Adobe Fonts without
font-display: swapwill block rendering. Custom code in the<head>can override this. - Render-blocking scripts. Any third-party script loaded synchronously in the
<head>will delay LCP. All non-critical scripts should be deferred or loaded viaasync.
CLS is affected by:
- Images without explicit width/height attributes. Webflow's image component sets these by default, but custom HTML embeds often don't.
- Web fonts causing layout shifts before they load. Again,
font-display: swapis the standard mitigation. - Dynamically injected content that pushes existing elements down the page.
INP is affected by:
- JavaScript execution time. Heavy GSAP animation timelines, large third-party scripts, and unoptimized custom interactions can all contribute to poor INP scores.
- Interaction handler efficiency. Event listeners attached to many DOM elements simultaneously can create bottlenecks on lower-end devices.
GSAP and Custom Interactions: Performance Considerations
Webflow's native interactions engine is built on Web Animations API and is generally performant for standard scroll-triggered animations and state transitions. For more complex animation work — staggered timelines, scroll-scrubbed sequences, morphing paths — GSAP is the standard choice, and it's one we use extensively at werun.dev.
GSAP animations should be built with GPU-accelerated properties in mind:
// Prefer transform and opacity — these run on the compositor thread
gsap.to('.hero-element', {
  y: -40,
  opacity: 0,
  duration: 0.6,
  ease: 'power2.out'
});

// Avoid animating layout-triggering properties
// top, left, width, height, margin — these force reflow
gsap.to('.hero-element', {
  top: '-40px', // Don't do this
  duration: 0.6
});
For scroll-triggered animations, ScrollTrigger should be initialized after the DOM is fully loaded, and invalidateOnRefresh: true should be set for any pinned sections to prevent layout calculation errors on resize.
Image Optimization Strategy
Webflow's asset pipeline compresses and serves images via its CDN, but the platform does not automatically resize images to match the breakpoint at which they're displayed. A 4000px wide hero image uploaded without responsive variants will be served at full resolution on mobile unless you configure the responsive image settings in the element panel or handle this via custom srcset attributes in HTML embeds.
For CMS-driven image fields, Webflow supports URL-based image transformations through its CDN. You can append parameters to dynamically resize images:
<!-- Serve a 800px wide WebP version of a CMS image -->
<img src="{{ cms-image-field }}?w=800&q=80&auto=format"
     alt="{{ alt-text-field }}"
     loading="lazy" />
This technique is particularly useful in Collection List components where images are pulled from CMS fields and need to be sized appropriately for their display context without uploading multiple variants.
Security Architecture: What Webflow Handles and What You Own
Webflow's security posture is considerably stronger than most self-managed WordPress or custom server deployments by default, primarily because the attack surface is fundamentally different. A statically compiled site served from a CDN has no database to SQL-inject, no PHP interpreter to exploit, and no plugin ecosystem to compromise.
Platform-Level Security
Webflow manages the following security concerns at the infrastructure level:
- DDoS mitigation: Fastly's network provides volumetric DDoS protection by design. Distributed edge caching means that even a high-volume attack is absorbed across the network rather than hitting a single origin.
- WAF (Web Application Firewall): Enterprise plans include WAF capabilities. Standard plans rely on Fastly's edge filtering.
- TLS/SSL management: As covered above, certificates are auto-provisioned and renewed.
- Physical and network security: Inherited from AWS's SOC 2 Type II, ISO 27001, and PCI DSS compliant data centers.
- Platform authentication: Webflow's Designer and CMS Editor access is protected by two-factor authentication and team-level role permissions.
Security Responsibilities That Remain With You
The static-site security model does not eliminate all attack vectors. The following remain your responsibility:
Third-party scripts: Every script you embed — analytics, chat widgets, A/B testing tools, ad pixels — is a potential XSS vector. A compromised third-party CDN serving a script on your Webflow site can inject malicious code into your users' browsers. Subresource Integrity (SRI) hashes should be used wherever possible for externally hosted scripts:
<script
  src="https://cdn.example.com/library.min.js"
  integrity="sha384-[hash-value]"
  crossorigin="anonymous">
</script>
Form submissions and API endpoints: Webflow's native forms POST to Webflow's own servers, which provides basic spam filtering. But if you're routing form data to external APIs — Airtable, HubSpot, a custom webhook — you need to validate and sanitize inputs on the receiving end. Webflow itself does not sanitize form payloads before forwarding them.
CMS content and editor access: The Webflow CMS Editor grants publish rights to anyone with Editor access. For multi-editor setups, role permissions should be reviewed carefully. Content injection via the CMS (e.g., a compromised editor account inserting malicious script tags into rich text fields) is a real vector that platform-level security does not prevent.
Custom code embeds: Custom HTML/CSS/JS embeds in Webflow bypass the platform's standard rendering pipeline. Malicious or poorly written embed code can introduce XSS vulnerabilities, degrade performance, or break layout in ways that are difficult to debug. All custom code should go through the same review process as application code in any other context.
Compliance Considerations
For B2B companies in regulated industries — finance, healthcare, legal — Webflow's compliance posture matters at procurement. Webflow is SOC 2 Type II certified and GDPR-compliant as a data processor. The platform's Data Processing Agreement (DPA) is available for Enterprise customers and covers the handling of visitor data collected through Webflow forms and the CMS Editor.
For HIPAA-regulated data, Webflow is not a covered entity and does not sign Business Associate Agreements (BAAs). Any PHI collected through a Webflow site must be routed to a HIPAA-compliant third-party service — the form or interaction can live in Webflow, but the data storage and processing must happen elsewhere.
Architectural Patterns for Production Webflow Projects
Understanding Webflow's infrastructure is useful in isolation, but the real value comes from knowing how to architect projects that work with the platform's strengths and route around its constraints. The patterns below represent the approaches we apply at werun.dev for production Webflow builds.
Headless Webflow with Next.js or Astro
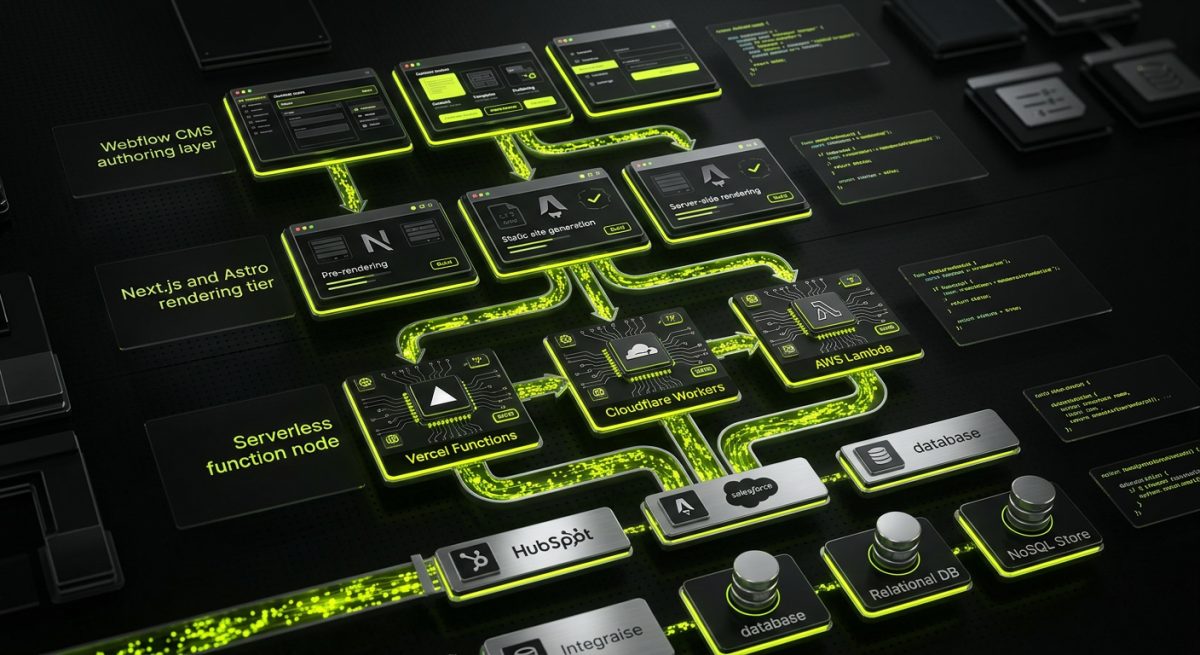
When a project's requirements exceed what Webflow's hosting and rendering model can support — server-side personalization, authenticated routes, complex API-driven data fetching — the right move is to decouple the CMS from the front-end. Webflow's CMS becomes a content authoring layer, and its content is consumed via the Webflow CMS API by a Next.js or Astro front-end deployed on Vercel or Cloudflare Pages.
This pattern gives you:
- Full control over rendering strategy (SSR, SSG, ISR)
- Server-side logic and middleware
- Custom caching headers and edge function behavior
- No Webflow hosting dependency for the live site
The trade-off is that the visual CMS Editor experience is lost — editors must use Webflow's CMS interface without seeing live previews on the actual front-end. For content-heavy B2B sites where editorial workflows matter, this trade-off needs to be evaluated carefully.
Middleware Integration Architecture
For Webflow sites that need to connect to CRMs, ERPs, payment systems, or internal tools without going fully headless, the standard pattern is:
Webflow Site
    │
    ├── Native Form → Webflow API → Zapier/Make → HubSpot/Salesforce
    │
    ├── Custom Form → Fetch POST → Serverless Function → Database/API
    │
    └── Memberstack/Outseta → Gated Content → External User DB
Serverless functions (Vercel Functions, Cloudflare Workers, AWS Lambda) act as a secure middleware layer between Webflow's front-end and your backend systems. API keys and sensitive credentials live in the serverless function's environment variables, never in Webflow's custom code embeds where they'd be exposed to the browser.
CMS Architecture for Editorial Scale
Webflow's CMS is powerful but has hard limits: 10,000 items per collection, 30 fields per collection, 20 collections per site (on Business plan). For sites that will grow into these limits, the CMS architecture needs to be planned before the first item is created.
Best practices for production CMS architecture:
- Reference fields over text fields: Use collection references to link related content rather than duplicating data across collections. This keeps content DRY and makes bulk updates manageable.
- Normalize taxonomy: Tags, categories, authors, and product types should be their own collections referenced from content collections — not multi-reference fields with free-form text.
- Plan for the API: If you'll ever consume CMS content via the API (for headless builds, mobile apps, or data exports), field names matter. Use consistent, lowercase, hyphenated slugs for field names from day one.
- Stage content with status fields: Webflow's draft/published toggle is binary. For complex editorial workflows, a "Status" select field (Draft, Review, Approved, Published) gives editors more granular workflow control, even if the actual publishing gate remains Webflow's native toggle.
At werun.dev, CMS architecture is treated as a first-class deliverable on every Webflow project — not an afterthought. The collections schema, field naming conventions, and reference structure are documented and reviewed before a single page template is built, because retrofitting a CMS architecture after content has been entered is significantly more expensive than getting it right at the start.
Performance Monitoring in Production
Webflow does not provide built-in performance monitoring or real user metrics (RUM). For production sites where performance is a business metric, you need to instrument this externally:
- Google Search Console: Core Web Vitals field data aggregated from Chrome users. The most authoritative source for real-world performance data.
- Cloudflare Web Analytics or Plausible: Privacy-first alternatives to GA4 with lower script overhead.
- SpeedCurve or Calibre: Continuous performance monitoring with alerting on regression. Worth the investment for high-traffic B2B sites.
- Sentry: JavaScript error tracking. Custom code embeds and GSAP interactions can fail silently in certain browser environments without error tracking in place.
The combination of Webflow's CDN infrastructure and a well-engineered build can consistently achieve Lighthouse scores in the 90–100 range on desktop and 80–95 on mobile — but only when performance is treated as a design constraint from the beginning of the project, not a post-launch optimization task.